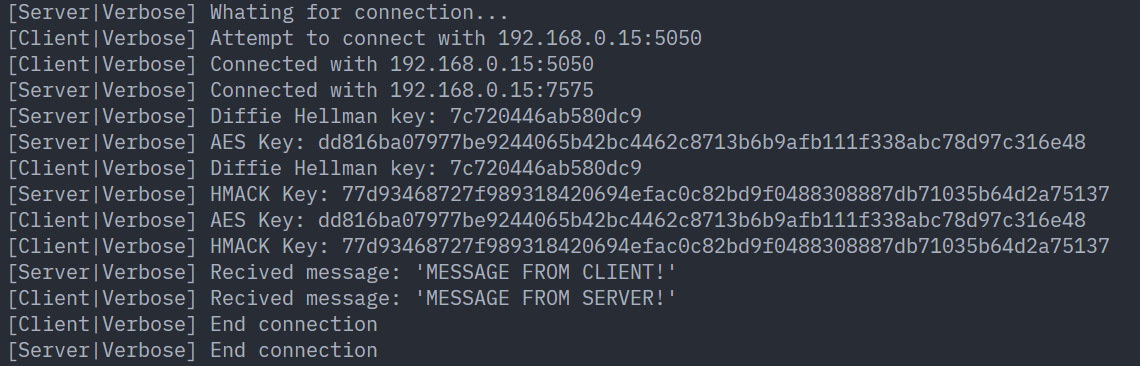
Summary
A Python-based secure messaging application using sockets. This project implements a custom cryptographic protocol designed from scratch to guarantee the three pillars of information security: Confidentiality, Integrity, and Authenticity. It includes a complete local simulation handling client and server threads.
Protocol Architecture
The communication protocol secures the channel in three phases:
- Mutual Authentication & Key Exchange: Client and server generate Diffie-Hellman key pairs and sign their public keys using ECDSA to prevent Man-in-the-Middle (MitM) attacks. Signatures are verified using public keys fetched locally or via GitHub profiles.
- Key Derivation: The shared seed is passed through PBKDF2 with unique salts to derive independent, cryptographically strong keys for AES encryption and HMAC.
- Secure Communication: Messages are encrypted using AES-GCM for confidentiality and appended with an HMAC-SHA256 tag to verify integrity and origin. Payloads are transmitted in Base64 as
(HMAC_TAG, IV, ENCRYPTED_MESSAGE).
Security Verification
The protocol’s effectiveness can be audited using Wireshark. While the initial TCP handshake and Diffie-Hellman parameters are visible during setup, all subsequent message payloads are obfuscated by AES-GCM encryption.